Almost every company today is talking about Artificial Intelligence. We see pilot projects, internal chatbots, early automation attempts, new tools, and ambitious strategic programs. At the same time, a second movement is growing within organizations: a creeping fear of losing control, data privacy breaches, liability, and flawed automated decisions.
This creates a frustrating contradiction.
On one hand, employees are urged to be innovative, work faster, experiment with AI, and unlock productivity. On the other hand, they are handed 24-page guidelines, paralyzing approval processes, blanket bans, and often no officially approved, viable alternatives to the tools they already use in their private lives.
This approach is fundamentally broken.
AI needs governance. But it doesn’t need bureaucracy that suffocates innovation. Excellent governance is not a roadblock—it is the safety railing that makes high speed possible in the first place.
👥 From Data Democratization to Accountability Democratization
In the previous step, we looked at data democratization. Companies must organize their data so employees are no longer trapped in departmental silos. Data must be discoverable, understandable, usable, and securely managed.
But with AI, we enter a new level of maturity.
When data is democratized, the responsibility of handling that data must be democratized too.
AI is not just an IT, Data Science, Legal, or Compliance project. It is actively used on the front lines: in Sales, Customer Service, Product Development, Marketing, Finance, HR, and Management.
Therefore, every employee must understand exactly what they can do with AI, what they cannot do, and where they need to tread carefully. They don’t need an unreadable policy document buried deep in the corporate intranet. They need short, practical, and logical rules for their daily workflows:
- Which data am I allowed to enter?
- Which tools are approved for my department?
- What workflows can I safely automate?
- When do I need a formal sign-off?
- Which AI outputs must I review before using them?
- Who ultimately owns the responsibility for the final decision?
🚫 Fear is the Silent Killer of AI Adoption
Many organizations severely underestimate the psychological factor of AI. Employees don’t just have technical questions; they have deep, unspoken concerns:
- “Am I even allowed to use this?”
- “Will I get fired if I accidentally paste the wrong data?”
- “Will AI be used to replace my job if I show how easily my tasks can be automated?”
These fears are real, and they decide whether your AI initiatives succeed or fail.
Good governance removes this anxiety. It doesn’t just say, “Be careful.” It says, “If you follow these clear guardrails, you are 100% safe.”
When structured correctly, governance is not a surveillance tool used against employees. It is a protective shield for them.
🕵️♂️ Bans Without Alternatives Invite “Shadow AI”
One of the most common mistakes companies make is issuing a blanket ban on external AI tools without offering a viable internal substitution.
Of course, a company cannot allow confidential customer data, intellectual property, or strategic business plans to be pasted into public, unsecured consumer AI models. That would be naive and highly dangerous.
But the answer cannot be a flat: “Do not use AI.”
Employees already know what is possible. They use ChatGPT, Claude, or Gemini at home. They know how instantly these tools can structure text, analyze code, or summarize complex information.
If they are forced to use slow, outdated, or non-existent tools at work while being pressured to deliver “more efficiency and innovation,” frustration sets in.
A ban without a substitute is not governance. It is a direct invitation to Shadow AI.
Employees will inevitably find workarounds. They will use personal accounts, poorly anonymize sensitive data, and copy-paste corporate information into unapproved systems. Not out of malice, but simply because they want to get their jobs done.
If you restrict external tools, you must provide an internal, secure alternative that is at least “good enough” so employees aren’t penalized for following the rules.
⚙️ Governance by Design: In the Flow of Work
Most compliance frameworks fail because they exist outside of the actual workflow. There are manuals, training videos, and checklists, but when an employee sits in front of a live task, they still don’t know what to do.
Modern AI governance must be embedded where the work actually happens.
We call this Governance by Design.
An employee shouldn’t have to read three legal PDFs just to figure out if they can summarize an email. The system itself should guide them:
- 🟢 This data class is permitted.
- 🔴 This sensitive database is locked.
- ⚠️ This generated output requires a human review.
- 📝 This automated action is being logged.
When guardrails are baked directly into the platforms, compliance stops being an administrative hurdle and becomes a natural, friction-free part of the job.
🤝 Compliance as an Innovation Partner
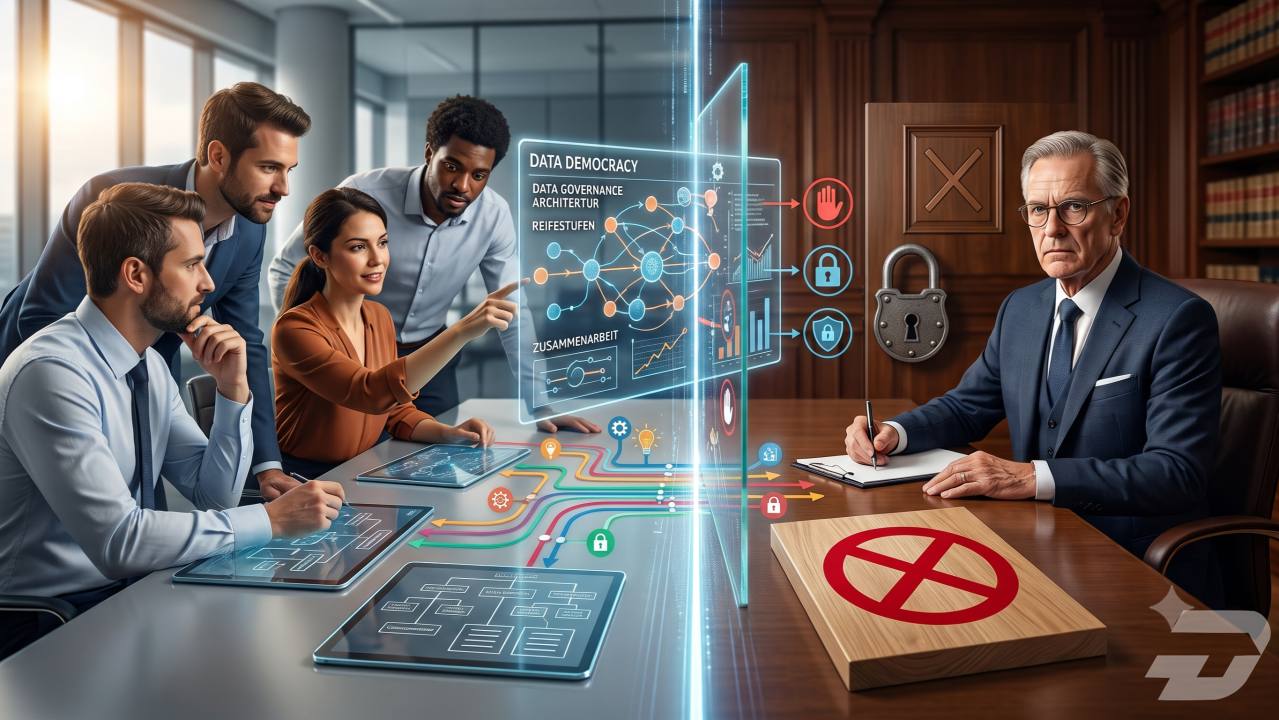
Historically, compliance has been trapped in a defensive, reactive role. They are called in at the very end of a project to review, audit, or flag risks. In innovation cycles, this creates a toxic pattern: the business wants speed, IT wants technical feasibility, and Compliance arrives late to say “No.”
For AI, this is a recipe for failure.
Because AI fundamentally changes data flows and decision-making, Compliance must be at the table from day one—not as an auditor, but as a co-creator.
The central question should never be: “Are we allowed to do this?”
The far better question is: “How can we design this so we can do it responsibly?”
This shifts the dynamic. Compliance is no longer seen as the “department of no,” but as an active partner that helps build structure, safety, and trust.
⚖️ Speed Demands Risk-Based Rules
AI models are not neutral, passive tools. They process data, generate automated recommendations, influence critical decisions, and can scale errors instantly. Because the stakes are high, clear roles must be established:
- Who is the model owner?
- Who is the data owner?
- Who has the authority to push a model to production?
- Who is accountable if the model hallucinates or generates a false decision?
However, responsibility must not lead to paralysis. A minor internal copywriting assistant does not need the same level of auditing as an AI system used to screen job applicants, approve credit lines, or analyze medical data.
Governance must be strictly risk-based.
- Low Risk: Simple, open guardrails for quick execution.
- High Risk: Robust, multi-layered audits and human-in-the-loop controls.
Many companies make the mistake of creating too many rules for harmless applications, and too few for critical ones. True governance knows the difference.
📝 The Two-Tier Model: Simple Rules, Deep Controls
To be effective, your daily AI policy should be simple enough to fit on a single page. Give your employees clear, repeatable principles they can memorize:
- Use only approved, secure corporate AI tools.
- Never enter personally identifiable or confidential data into public models.
- Always verify AI-generated facts before using them externally.
- Never let AI make final decisions that impact human lives without human oversight.
- Be transparent about where and how you use AI.
This doesn’t replace the complex technical controls running in the background. But it gives your workforce immediate direction, reduces anxiety, and builds confidence.
By separating your strategy into simple rules for the masses and robust, automated controls for the backend, you get the best of both worlds: safety and speed.
🎯 Bottom Line: Governance is a Leadership Mandate
Ultimately, AI governance is neither an IT task nor a legal chore. It is a leadership responsibility.
Leaders must decide how much risk the company is willing to accept, which tools will be funded, and how the bridge between innovation and control will be built.
Without governance, you get chaos. But with too much bureaucracy, you get complete stagnation.
The goal is not absolute control. The goal is responsible speed.
Companies that succeed with AI don’t build compliance theater. They build secure data pathways, establish clear accountability, and foster a culture where employees can innovate without fear.
Governance is not the enemy of innovation -> it is the very engine that allows it to scale.
image sources
- 1784049428210: Generated with Nano-Banana

Join the discussion